All Categories
Featured
Table of Contents
To asses threat Waydev enables you to determine how likely it is a particular devote will trigger issues. In this case, there are specific data points that you ought to take into consideration, such as the commit's size, how far do the changes spread out, in addition to the changes' depth. Continuous Integration (CI) and Continous Advancement (CD) are important in today's engineering community since they ensure that your team provides software in an iterative type.

Our option instantly gathers information from the Constant Combination and Continous Advancement pipelines and tracks Gitlab repos, allowing you to analyze information without requiring any kind of manual input. This is an outstanding way to keep an eye on DevOps efficiency by focusing on DORA metrics. By automating these procedures and measurements, you may have a clear view of how release is going, examine what effects burn-down rates, what triggers bottlenecks, and how to fix them.
This allows you to reallocate resources to ship on time or enhance expenses and interact job status to organization leaders. When done right, the aligns organization requirements with technology processes, enabling Engineering Supervisors to optimize performance and evaluate risks.
IT governance focuses on setting tactical direction, policies, and oversight. Training should cover framework concepts, brand-new policies and procedures, governance functions and obligations, and any governance tools or systems being carried out.
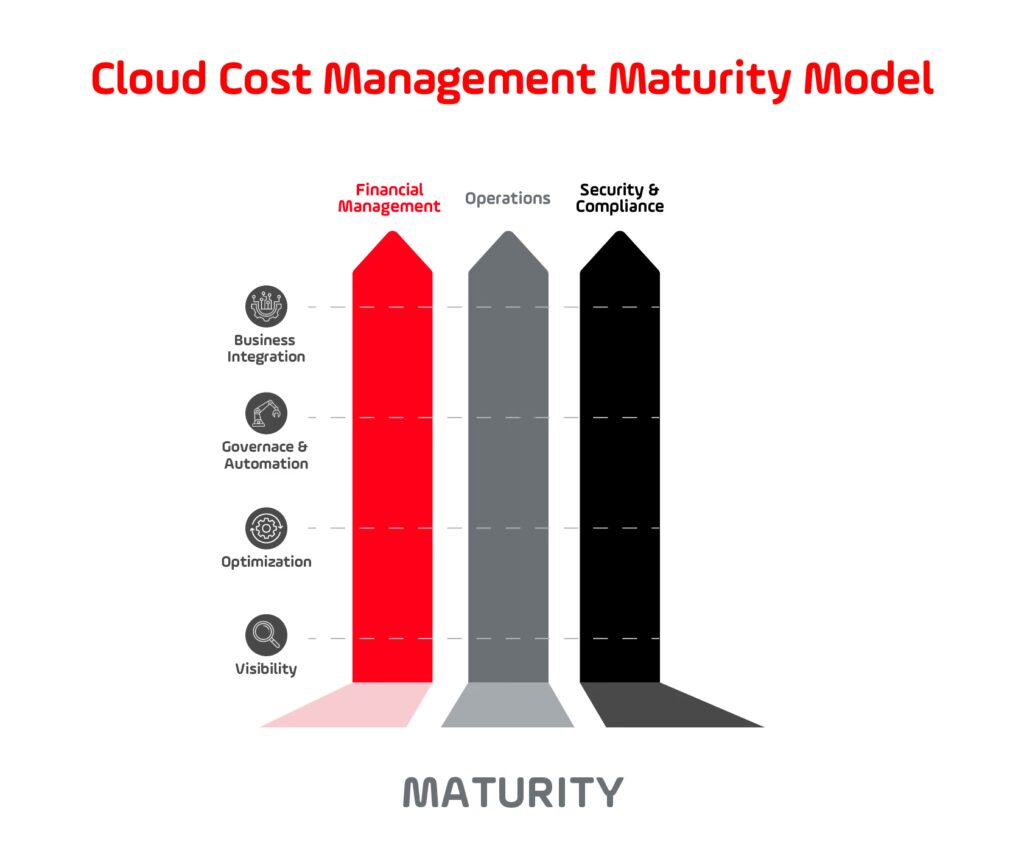
Key Benefits of Enterprise Resource Optimization
Threat management determines risks, assesses impacts, and develops mitigation strategies. It ensures governance effectively deals with information security, disaster healing, and regulatory compliance.
IT governance handles governance and threats while maintaining compliance with market and federal government regulations. Optimizing IT governance requires the best mix of IT investments, policy and personnel.
It is increasingly a component of DevOps groups responsible for IT operations. DevOps groups interact more efficiently to produce, test and provide software. As companies increase their IT investments, the value of a strong IT governance policy boosts. Chief info officers (CIOs) drive IT governance technique alongside other key stakeholders in the C-suite.
Strategic Budget Planning for Modern Cloud EnvironmentsEffective IT governance aligns innovation choices with organization technique, manages danger, and ensures IT resources are used effectively. This guide covers each step in practical information, along with the frameworks, tools, and best practices IT leaders utilize today.
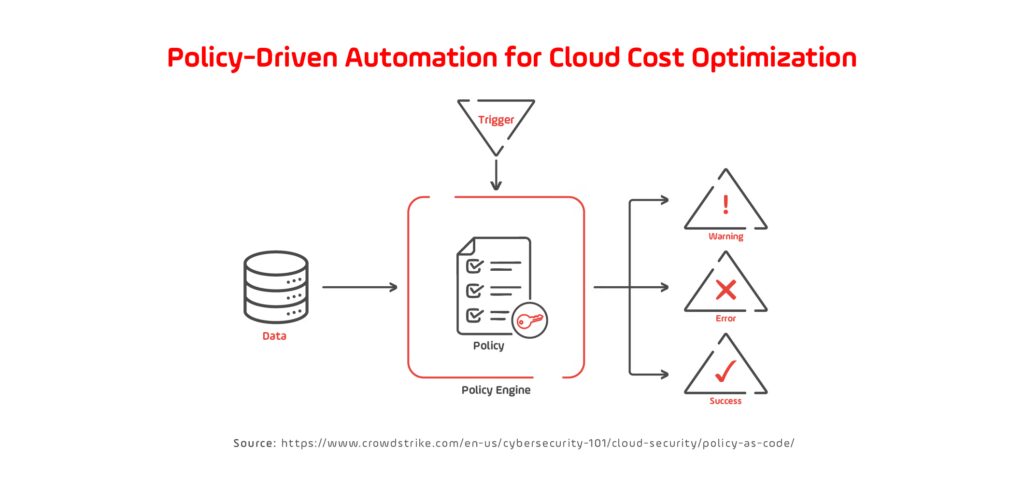
Strategic Infrastructure Resource Allocation for Efficiency
Appoint clear accountability for each governance domain. Framework Primary focus Best matched for IT governance and management, risk control, audit readiness Big enterprises, controlled industries IT service management aligned to company needs Organizations with a mature IT service function International standards for IT service management and business IT governance Organizations looking for licensed, globally acknowledged governance CMMI(Capability Maturity Design Combination)Process enhancement rated on a scale of 1 to 5 Organizations benchmarking and enhancing development or delivery ability COSO (Committee of Sponsoring Organizations of the Treadway Commission)Internal control and enterprise risk management Organizations prioritizing financial controls and fraud deterrence CIS( Center for Internet Security)Controls Cybersecurity and facilities durability Organizations strengthening technical security posture Many organizations combine structures. Governance that is not measured does not improve.

Latest Posts
Refining Resource Allocation to Reduce Excess IT Costs
How to Optimize Cloud Budgets in 2026
Is Your 2026 IT Spending Ready?