All Categories
Featured
Table of Contents
To asses risk Waydev enables you to measure how most likely it is a particular dedicate will trigger problems. In this case, there specify data points that you should take into consideration, such as the devote's size, how far do the changes spread, along with the modifications' depth. Continuous Combination (CI) and Continous Development (CD) are important in today's engineering ecosystem since they guarantee that your team delivers software in an iterative kind.
Navigating 2026 IT Finance Frameworks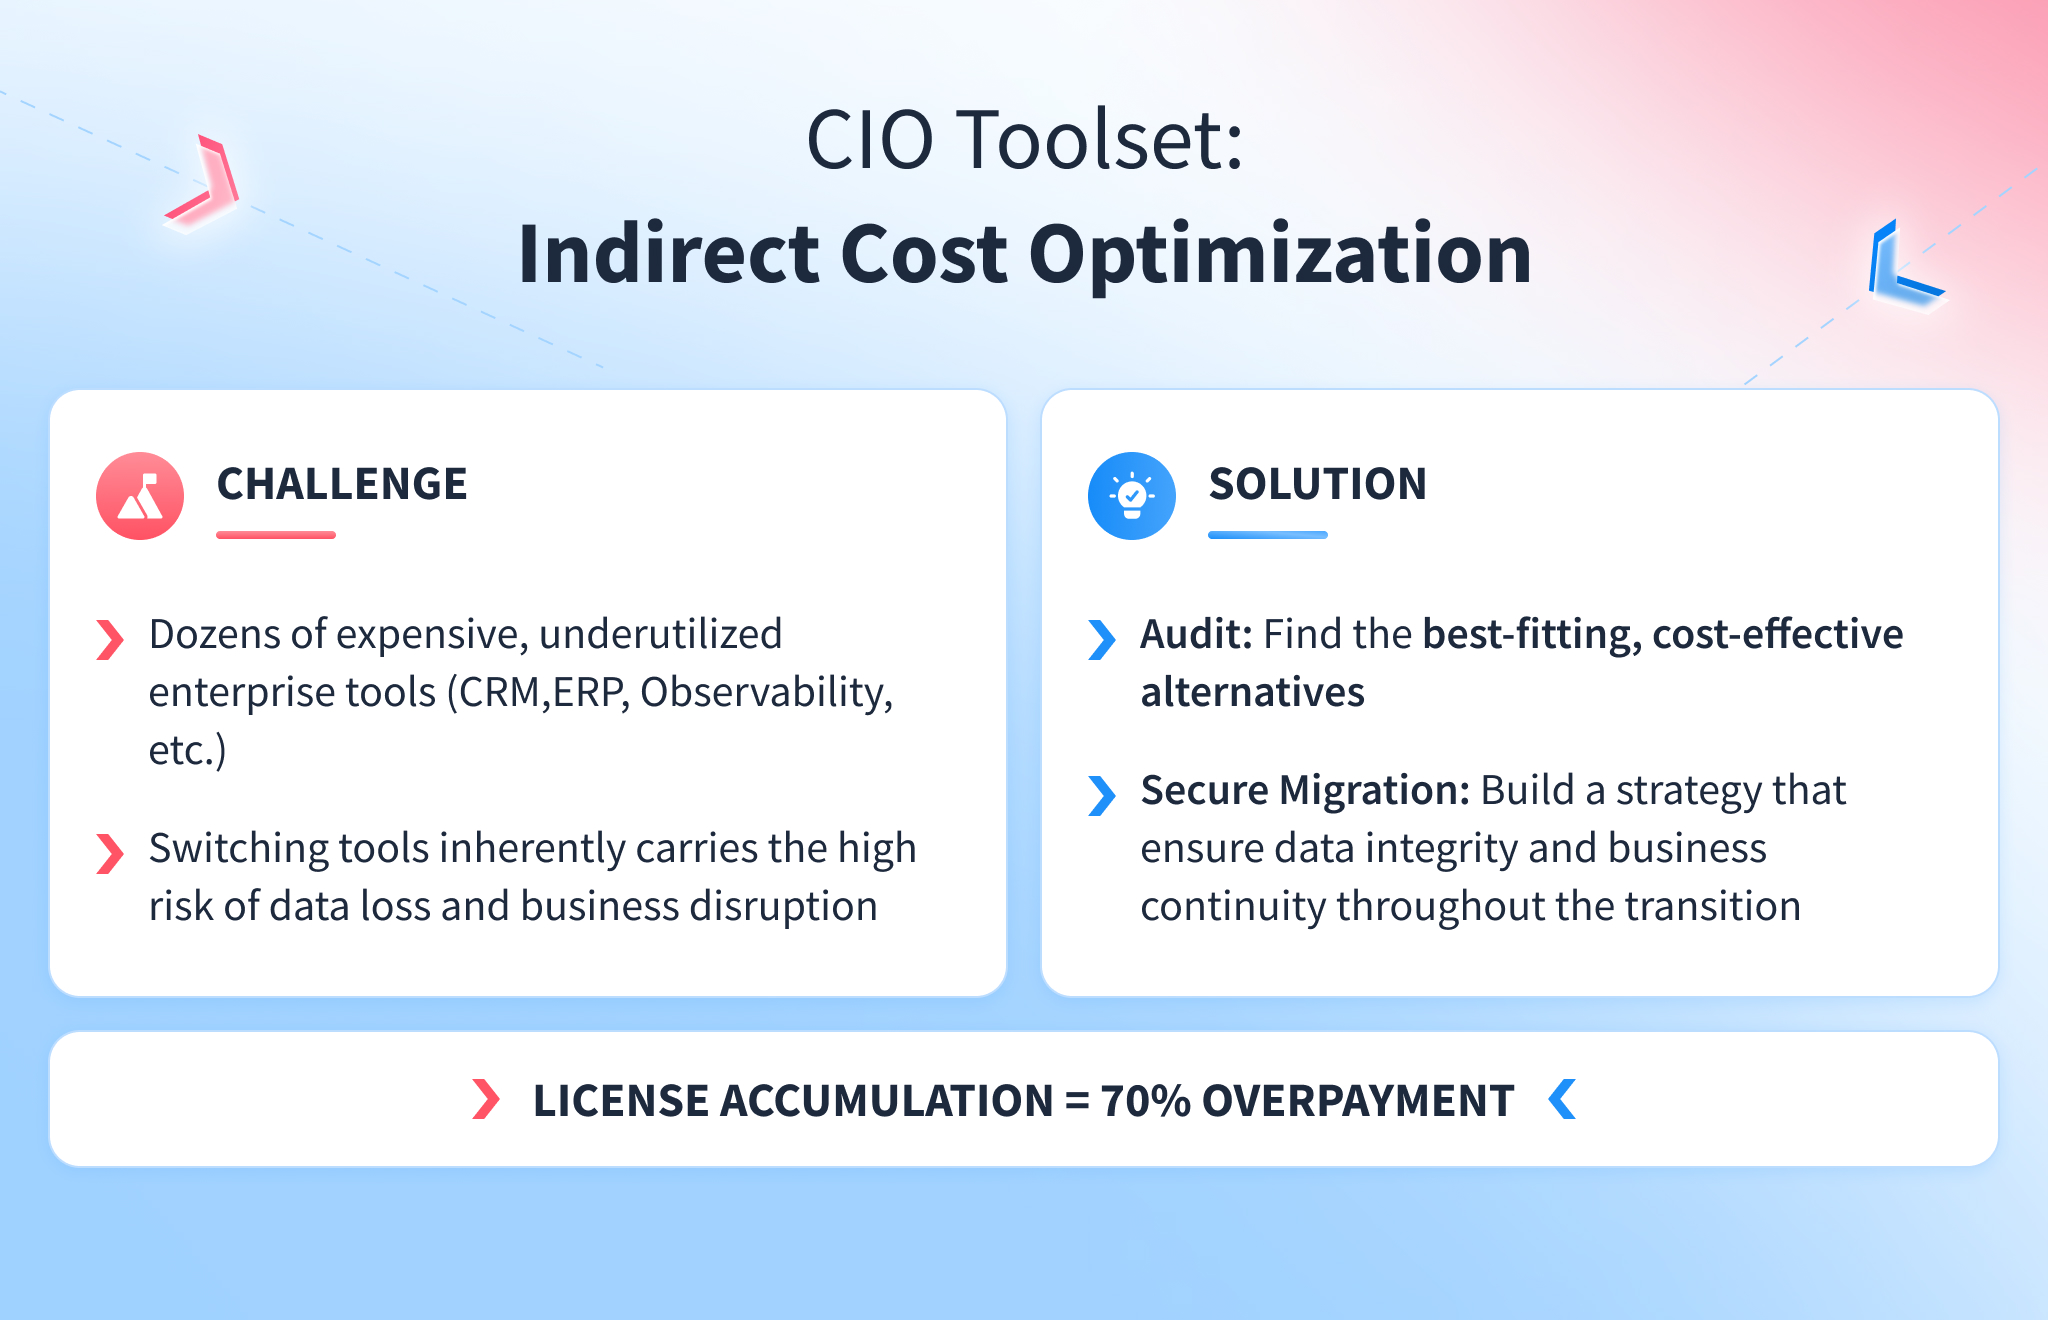
Our option immediately gathers information from the Constant Combination and Continous Development pipelines and tracks Gitlab repos, allowing you to evaluate info without needing any type of manual input. This is an outstanding method to monitor DevOps efficiency by focusing on DORA metrics. By automating these procedures and measurements, you might have a clear view of how deployment is going, evaluate what effects burn-down rates, what causes bottlenecks, and how to solve them.
With Waydev's Task Costs report, you have constant insights on how work is advancing and how things look financially. This allows you to reallocate resources to deliver on time or optimize costs and interact project status to magnate. When done right, the aligns business requirements with innovation processes, making it possible for Engineering Supervisors to enhance efficiency and examine risks.
IT governance focuses on setting tactical instructions, policies, and oversight. Training should cover structure concepts, new policies and treatments, governance functions and duties, and any governance tools or systems being implemented.
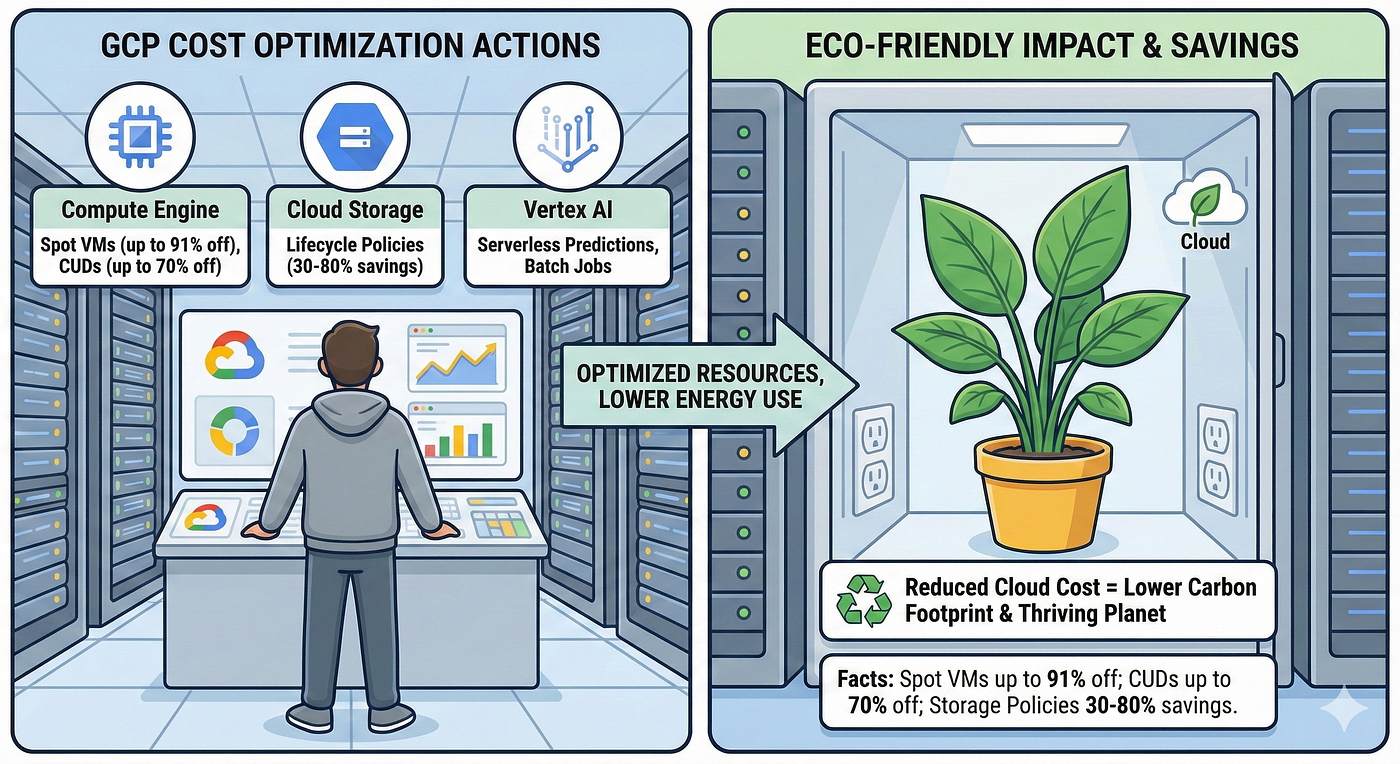
Is the 2026 Cloud Budget Ready for Scale?
More frequent evaluations might be required for fast-changing environments. KPIs to measure efficiency include IT cost optimization, IT and company technique positioning, user complete satisfaction, project ROI, and adherence to service levels. Danger management determines dangers, assesses impacts, and establishes mitigation techniques. It makes sure governance properly deals with info security, disaster recovery, and regulatory compliance.
Efficient IT governance is a crucial component of overall service strategy and business governance as a governance, threat and compliance (GRC) policy. IT governance handles governance and dangers while preserving compliance with industry and government regulations. Enhancing IT governance needs the right mix of IT financial investments, policy and personnel. It helps organizations match their IT objectives with organization goals.
As companies increase their IT financial investments, the significance of a strong IT governance policy increases. Chief details officers (CIOs) drive IT governance technique alongside other essential stakeholders in the C-suite.
Scaling Infrastructure Expenditures in 2026In this articleWhat is IT governance and why does it matter?Why worksIT governance important for business success?What are the 5 steps to implement reliable IT governance?What are the IT governance best practices that drive results?How does IT governance work for small businesses?Why well-established IT governance is a service benefit Reliable IT governance lines up technology decisions with business technique, controls danger, and ensures IT resources are utilized effectively. This guide covers each step in useful information, in addition to the frameworks, tools, and best practices IT leaders utilize today.
Key Benefits of Automated Cost Governance
Assign clear responsibility for each governance domain. Structure Main focus Finest fit for IT governance and management, risk control, audit readiness Large business, controlled industries IT service management lined up to organization needs Organizations with a fully grown IT service function International standards for IT service management and corporate IT governance Organizations seeking certified, internationally acknowledged governance CMMI(Ability Maturity Design Combination)Process enhancement ranked on a scale of 1 to 5 Organizations benchmarking and enhancing advancement or shipment ability COSO (Committee of Sponsoring Organizations of the Treadway Commission)Internal control and enterprise risk management Organizations prioritizing monetary controls and scams deterrence CIS( Center for Web Security)Controls Cybersecurity and facilities resilience Organizations strengthening technical security posture Numerous companies combine frameworks. Governance that is not measured does not improve.

Latest Posts
Refining Resource Allocation to Reduce Excess IT Costs
How to Optimize Cloud Budgets in 2026
Is Your 2026 IT Spending Ready?